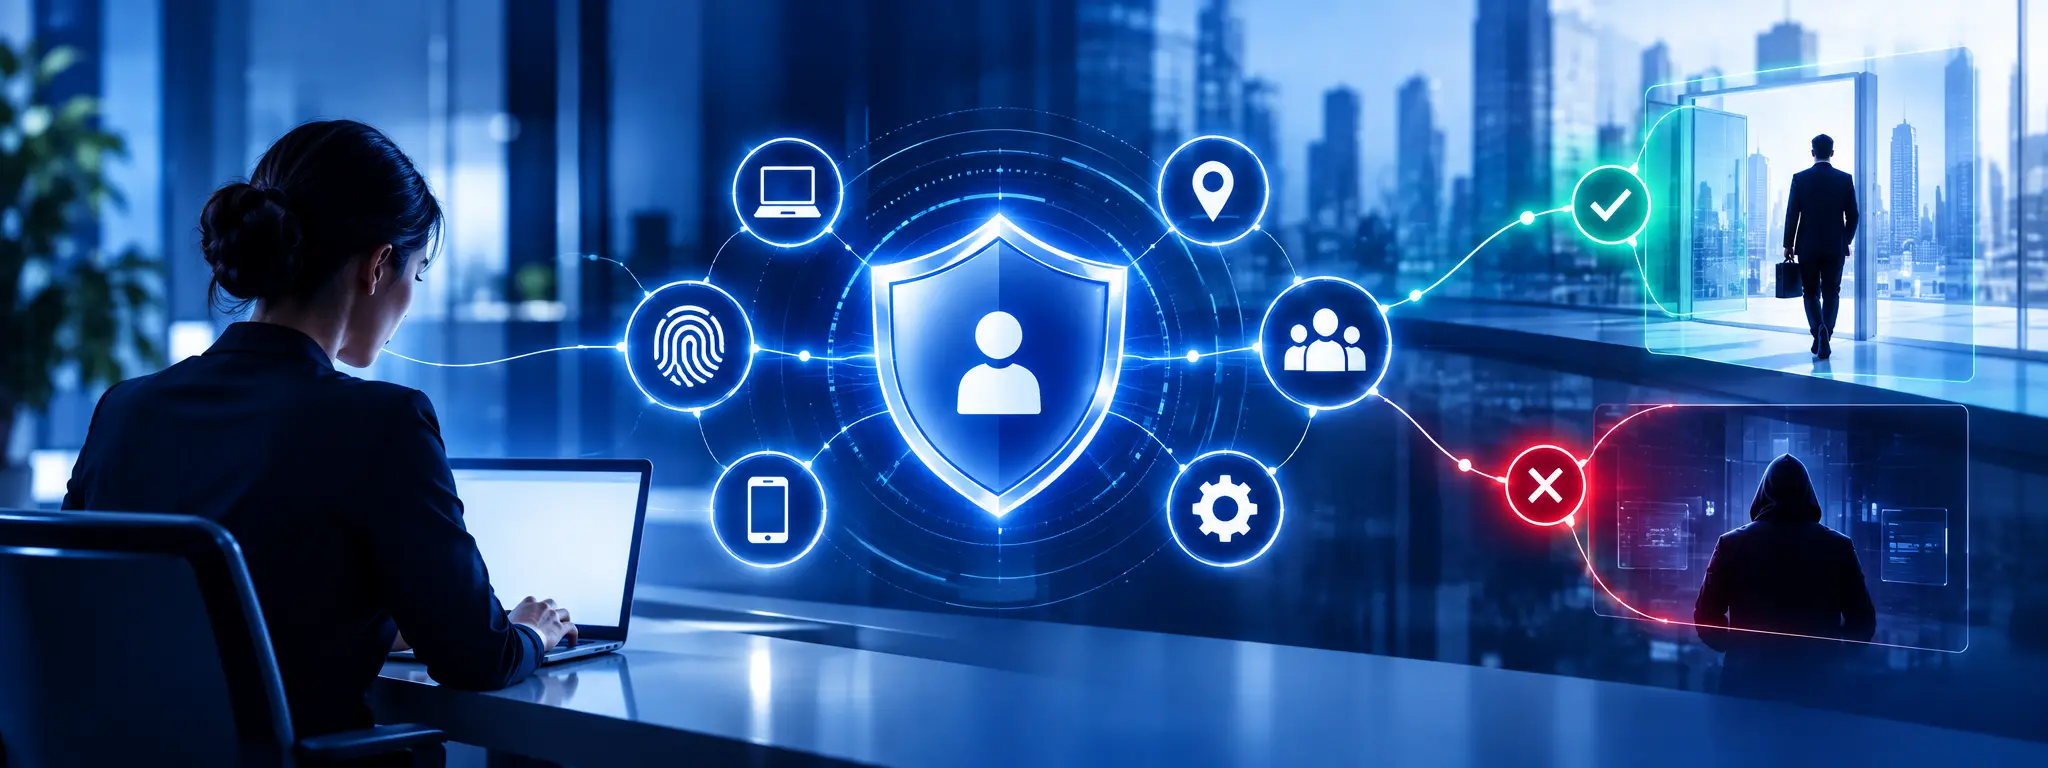
Static security policies that simply verify a username, password, and even multi-factor authentication (MFA) at login are no longer enough. Attackers can steal credentials, hijack sessions, and move laterally within networks after successful authentication. This is why Adaptive Access Controls, adaptive access management, and zero trust access control have become essential components of modern cybersecurity strategies.
By analysing real-time signals such as user behaviour, device health, location, network, time of access, and risk level, organisations can continuously determine whether a user should be granted, restricted, or denied access. The result is stronger security with a seamless user experience.
Table of Contents
- What Are Adaptive and Risk-Based Access Controls?
- Why Traditional Access Controls Are No Longer Enough
- How Adaptive Access Controls Evaluate Risk in Real Time
- How Adaptive Access Controls Improve User Experience
- Adaptive Access Controls and Zero Trust Security
- Key Features to Look for in an Adaptive Access Control Solution
- Common Implementation Mistakes
- Best Practices
- How Trevonix Helps Organisations
- Conclusion
What Are Adaptive and Risk-Based Access Controls?
Understanding Modern Access Control
Adaptive Access Controls are intelligent security policies that adjust authentication and authorisation requirements based on real-time risk. Instead of applying identical security measures to every login attempt, adaptive access management evaluates multiple contextual factors before making an access decision.
This modern approach combines context aware access, adaptive authentication, and risk based access control to provide stronger protection without creating unnecessary friction.
How Risk-Based Access Decisions Work
Every login request is assigned a risk score using factors such as:
- User identity
- Device trust
- Geographic location
- IP reputation
- Time of access
- User behaviour
- Application sensitivity
If the risk remains low, access is granted immediately. If the risk increases, risk based authentication may require additional verification before access is approved.
The Difference Between Static and Dynamic Access Controls
Traditional policies treat every login the same.
By contrast, dynamic access control continuously evaluates risk and adjusts permissions throughout the session. This enables organisations to apply Adaptive Access Controls without disrupting legitimate users.
Why Traditional Access Controls Are No Longer Enough
The Shift to Identity-Centric Attacks
Cybercriminals increasingly target identities rather than infrastructure. Stolen passwords, phishing attacks, session tokens, and compromised accounts allow attackers to bypass perimeter security.
This makes adaptive access management far more effective than relying solely on passwords.
Limitations of Static Authentication
Traditional authentication only validates identity at the beginning of a session.
Once authenticated, users often retain unrestricted access even if their risk level changes.
Challenges in Hybrid and Remote Work Environments
Employees now access business systems from multiple devices, locations, and networks. Static rules cannot accurately assess these constantly changing environments.
Using context aware access enables organisations to make smarter security decisions based on current conditions.
Credential Theft and Session Hijacking Risks
Even when credentials are valid, attackers may attempt session hijacking or privilege escalation.
This is why continuous access evaluation has become a critical security capability.
How Adaptive Access Controls Evaluate Risk in Real Time
Understanding Risk-Based Authentication
What Is Risk-Based Authentication?
Risk based authentication analyses contextual signals before determining the authentication requirements for each login attempt.
Unlike fixed MFA policies, authentication adapts according to calculated risk.
How Authentication Requirements Change Based on Risk
For example:
- Trusted device + familiar location = password only
- New device = MFA required
- Suspicious location = biometric verification
- High-risk activity = access blocked
This intelligent risk based access control improves security while reducing unnecessary authentication requests.
The Role of Adaptive Step-Up Authentication
What Is Step-Up Authentication?
Step-up authentication introduces additional verification only when required.
Instead of challenging every user equally, adaptive authentication requests stronger verification only for higher-risk situations.
When Additional Verification Is Required
Additional checks may include:
- Push notification approval
- Biometrics
- Security keys
- One-time passwords
Balancing Security and User Convenience
By using Adaptive Access Controls, organisations avoid unnecessary MFA while maintaining strong protection.
Continuous Access Evaluation and Policy Enforcement
Why One-Time Authentication Is Insufficient
A user's risk profile can change after login.
Continuous Verification in Modern Security
Continuous access evaluation monitors users throughout active sessions.
Monitoring Risk Throughout the User Session
Risk signals may include:
- Device becoming unmanaged
- VPN disconnecting
- Impossible travel
- Malware detection
- Abnormal behaviour
Responding to Changing Risk Conditions
If risk increases, dynamic access control automatically:
- Requests additional authentication
- Limits access
- Ends the session
- Blocks sensitive actions
How Adaptive Access Controls Improve User Experience
One of the biggest advantages of Adaptive Access Controls is balancing security with usability.
Benefits include:
- Reducing unnecessary MFA prompts through intelligent adaptive authentication
- Minimising authentication fatigue using risk based authentication
- Supporting productivity for hybrid workers with context aware access
- Providing seamless access for trusted users through adaptive access management
Rather than interrupting every employee, security measures are applied only when genuine risk exists.
Adaptive Access Controls and Zero Trust Security
Modern zero trust access control assumes no user or device should be trusted automatically.
Adaptive security strengthens Zero Trust by providing:
- Continuous identity verification
- Least privilege access
- Real-time risk based access control
- Intelligent dynamic access control
- Ongoing continuous access evaluation
- Secure cloud and hybrid access
Together, these capabilities create a resilient identity-first security model.
Key Features to Look for in an Adaptive Access Control Solution
An enterprise-grade solution should include:
- Intelligent adaptive authentication
- Real-time context aware access
- Automated risk based authentication
- Behaviour analytics
- Device trust assessment
- AI-powered risk scoring
- Session monitoring
- Continuous access evaluation
- Integration with identity providers
- Support for zero trust access control
Common Mistakes Organisations Make When Implementing Risk-Based Access Controls
Many organisations fail to maximise the value of Adaptive Access Controls because they:
- Apply identical policies to every application
- Ignore behavioural analytics
- Depend solely on passwords and MFA
- Fail to update risk policies
- Overlook dynamic access control
- Neglect continuous access evaluation
- Create excessive authentication friction
Best Practices for Implementing Adaptive Access Controls
Successful implementation includes:
- Establishing a strong identity foundation
- Defining risk-based policies
- Continuously reviewing access decisions
- Using adaptive access management across cloud and on-premises applications
- Combining adaptive authentication with behavioural analytics
- Applying context aware access for every access request
- Enforcing zero trust access control across the organisation
How Trevonix Helps Organisations Implement Adaptive and Risk-Based Access Controls
Trevonix enables organisations to modernise identity security through intelligent Adaptive Access Controls, advanced adaptive access management, and enterprise-grade zero trust access control solutions.
By combining risk based access control, risk based authentication, adaptive authentication, context aware access, dynamic access control, and continuous access evaluation, Trevonix helps organisations make accurate access decisions in real time while maintaining an excellent employee experience.
As part of its comprehensive identity security strategy, Trevonix also supports organisations in implementing a robust Zero Trust Identity Architecture, helping businesses continuously verify users, enforce least-privilege access, and protect critical applications across cloud, hybrid, and on-premises environments.
Conclusion
As identity attacks become increasingly sophisticated, traditional authentication can no longer provide adequate protection. Modern organisations require security that continuously evaluates risk rather than relying on a single login event.
Adaptive Access Controls, supported by adaptive access management and zero trust access control, enable organisations to make intelligent, context-driven access decisions without compromising productivity. By leveraging risk based access control, adaptive authentication, context aware access, risk based authentication, dynamic access control, and continuous access evaluation, businesses can reduce security risks while delivering a seamless experience for trusted users.
Organisations that embrace adaptive, identity-centric security today will be better prepared to defend against evolving cyber threats, strengthen compliance, and support a secure digital workforce for the future.