Who, exactly, is acting?
For identity and security teams, this is more than a question of authentication. An agent can be authenticated and still have too much authority. It can have legitimate access and still use that access in an unintended context. And when an agent acts on behalf of a person, the organisation needs to preserve the relationship between the human, the agent and the action.
That is where identity becomes central to AI governance.
Key Takeaways
- AI agents introduce a new class of enterprise actor whose access and actions need to be governed.
- Authentication alone is not enough; organisations need to understand authority, delegation and context at the time an agent acts.
- Existing identity disciplines such as least privilege, lifecycle management, access governance and auditability remain relevant, but need to extend to autonomous and non-human actors.
- Board-level AI governance ultimately depends on whether an organisation can establish who or what acted, under whose authority, what it was allowed to do and what happened as a result.
From AI that assists to AI that acts
Much of the early enterprise conversation around generative AI focused on copilots and assistants. These systems helped people find information, draft content or complete tasks, while the human remained responsible for taking the final action.
Agentic AI changes that relationship.
An agent can be given an objective and then determine a sequence of actions to achieve it. Depending on the implementation, those actions may span applications, APIs, data stores and other agents.
That creates a different security boundary.
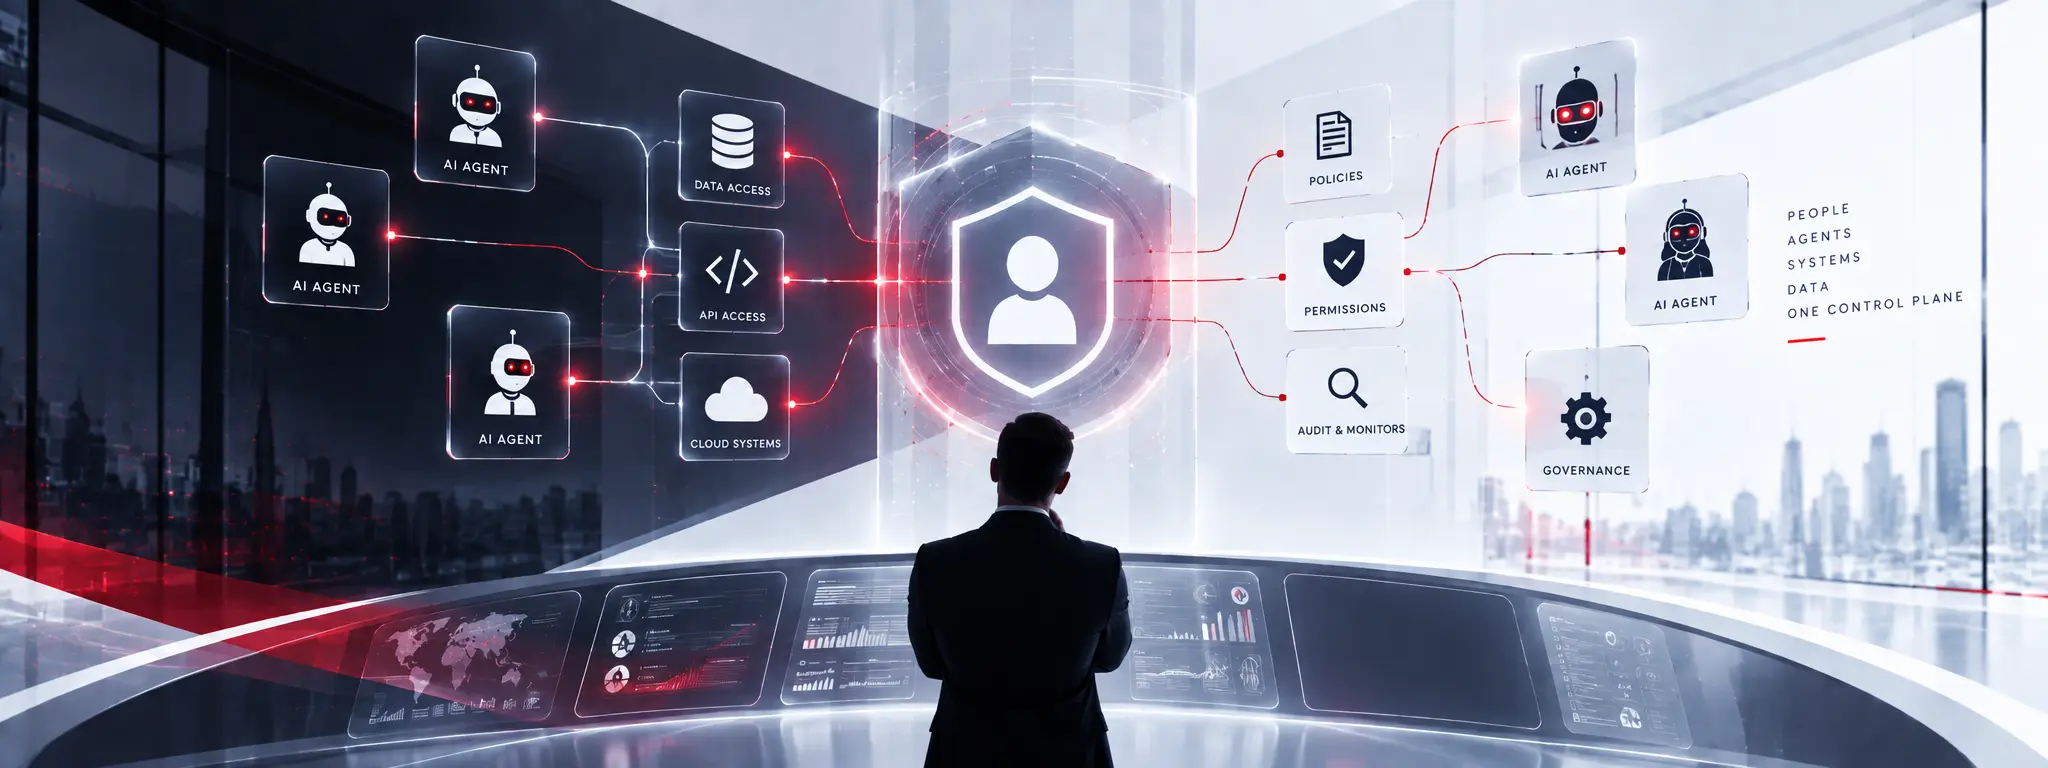
The question is no longer simply whether an employee is authorised to access an application. It is whether the agent acting on that employee's behalf is authorised to perform a particular action, against a particular resource, in a particular context.
This distinction is important because the same underlying user authority should not automatically translate into unrestricted agent authority.
The identity problem is really an authority problem
Identity has traditionally provided the foundation for answering three questions:
Who are you?
What are you allowed to access?
Who is accountable for that access?
Agentic systems add another layer:
Who are you acting for, and what authority has been delegated to you?
That relationship needs to be explicit.
An agent should not need to impersonate a person or inherit a broad set of human credentials simply because it is acting on that person's behalf. A governed model instead establishes the agent as a distinct non-human identity and defines the relationship between the agent, its owner or sponsor, the human principal and the resources it can access.
This is where established identity principles remain highly relevant.
Least privilege still matters. Lifecycle management still matters. Access reviews still matter. Auditability still matters.
What changes is the actor — and the speed and scale at which that actor can operate.
Static access is not enough when actions happen at runtime
Traditional access decisions are often made when an account, role or entitlement is provisioned.
That model becomes harder to rely on when an agent can make decisions dynamically.
An agent may be authorised to access a system, but whether it should perform a particular action can depend on the user it represents, the resource involved, the sensitivity of the data, the action being requested and the surrounding context.
Runtime authorisation allows those conditions to be evaluated when the action occurs.
Ping Identity's current approach to agent identity places particular emphasis on runtime identity and delegated authority for this reason: the goal is to connect an agent's action to the human or business principal behind it while applying fine-grained policy at the point of action.
The broader principle is technology-independent.
An agent's authority should be explicit, constrained and evaluated in context.
Governance has to follow the agent throughout its lifecycle
There is another problem that is easy to overlook.
An agent's risk does not end when it is deployed.
Its purpose can change. Its owner can change. New tools can be connected. Its permissions can expand. An experiment can become a production workflow.
This is familiar territory for identity governance teams.
Organisations already have processes for provisioning identities, reviewing access, managing changes and removing access when it is no longer required. Those disciplines provide an important foundation for governing AI agents.
The challenge is extending them to a new class of non-human identity.
An organisation should be able to maintain a reliable record of its agents, their owners, their purpose, their permissions and their lifecycle state. When an agent is retired, its identity and delegated permissions should not remain active. When its purpose changes, its access should be reassessed.
Visibility and governance therefore become prerequisites for scale.
When an AI incident becomes a board issue
Consider a scenario in which an AI agent has access to a customer system and a connected business application.
The agent is compromised or manipulated and performs an action outside its intended purpose.
The immediate questions may be technical:
What happened?
Which API was called?
Which credentials were used?
But the executive questions arrive quickly:
Who authorised the agent?
Why did it have that access?
Was the action within the agent's intended authority?
Who was accountable for the agent?
Could the organisation have stopped the action?
Could it prove what happened?
These are governance questions.
And they point to an important shift in the role of identity.
Identity is not simply the mechanism used to authenticate an agent. It provides the context required to establish accountability around autonomous action.
From security control to governance control
This is why identity is increasingly becoming part of the AI governance conversation.
AI governance establishes the principles and policies an organisation wants to follow.
Identity and authorisation help turn those principles into enforceable decisions.
If an organisation's policy says an agent should only access a particular class of information, identity and authorisation controls can help enforce that boundary.
If policy says an agent may act on behalf of a user only within a defined scope, delegation and runtime controls can help establish that relationship.
If policy requires accountability, identity and audit records can provide evidence of who or what acted and under whose authority.
The objective is not to slow down AI adoption.
It is to make greater autonomy possible without losing control.
The questions boards should be asking
Boards do not need to design an organisation's agent architecture. They do, however, need confidence that management understands the risks created when software begins to act autonomously.
A useful starting point is to ask:
- Do we know which AI agents are operating across the organisation?
- Does each agent have an accountable owner?
- Do we know what authority has been delegated to each agent?
- Can access be limited to what the agent needs for its purpose?
- Can we determine what an agent did and under whose authority it acted?
- Can its access and delegated authority be changed or revoked when circumstances change?
The answers will vary by organisation and use case.
But the underlying principle is becoming harder to ignore.
As AI moves from generating content to taking action, identity becomes part of the mechanism through which an organisation establishes trust, authority and accountability.
The organisations that get this right will not necessarily be the ones that deploy the fewest agents.
They will be the ones that can give their agents enough authority to be useful while retaining enough control to know when that authority is appropriate.
That is the path from breach to board-ready: making autonomy governable.
From Breach to Board-Ready: A Governance Playbook for Agentic AI
Discover how identity-first governance can help organisations secure AI agents, enforce least privilege and strengthen enterprise oversight.